
How a 40-Person Shop Can Cut Scope From 180 Assets to 22
Every asset inside your boundary carries a cost. Scope isn’t something you discover. It’s something you design, and the size of the boundary sets the bill.
The quote comes back, and the owner reads it twice to be sure the number is real. Every workstation, every server, every printer and phone in the building got swept into the assessment, and the price reflects all of it. That’s how a lot of CMMC projects begin: with a very bad afternoon.
It doesn’t have to. The difference between that afternoon and a manageable project usually comes down to one decision nobody told the owner they get to make.
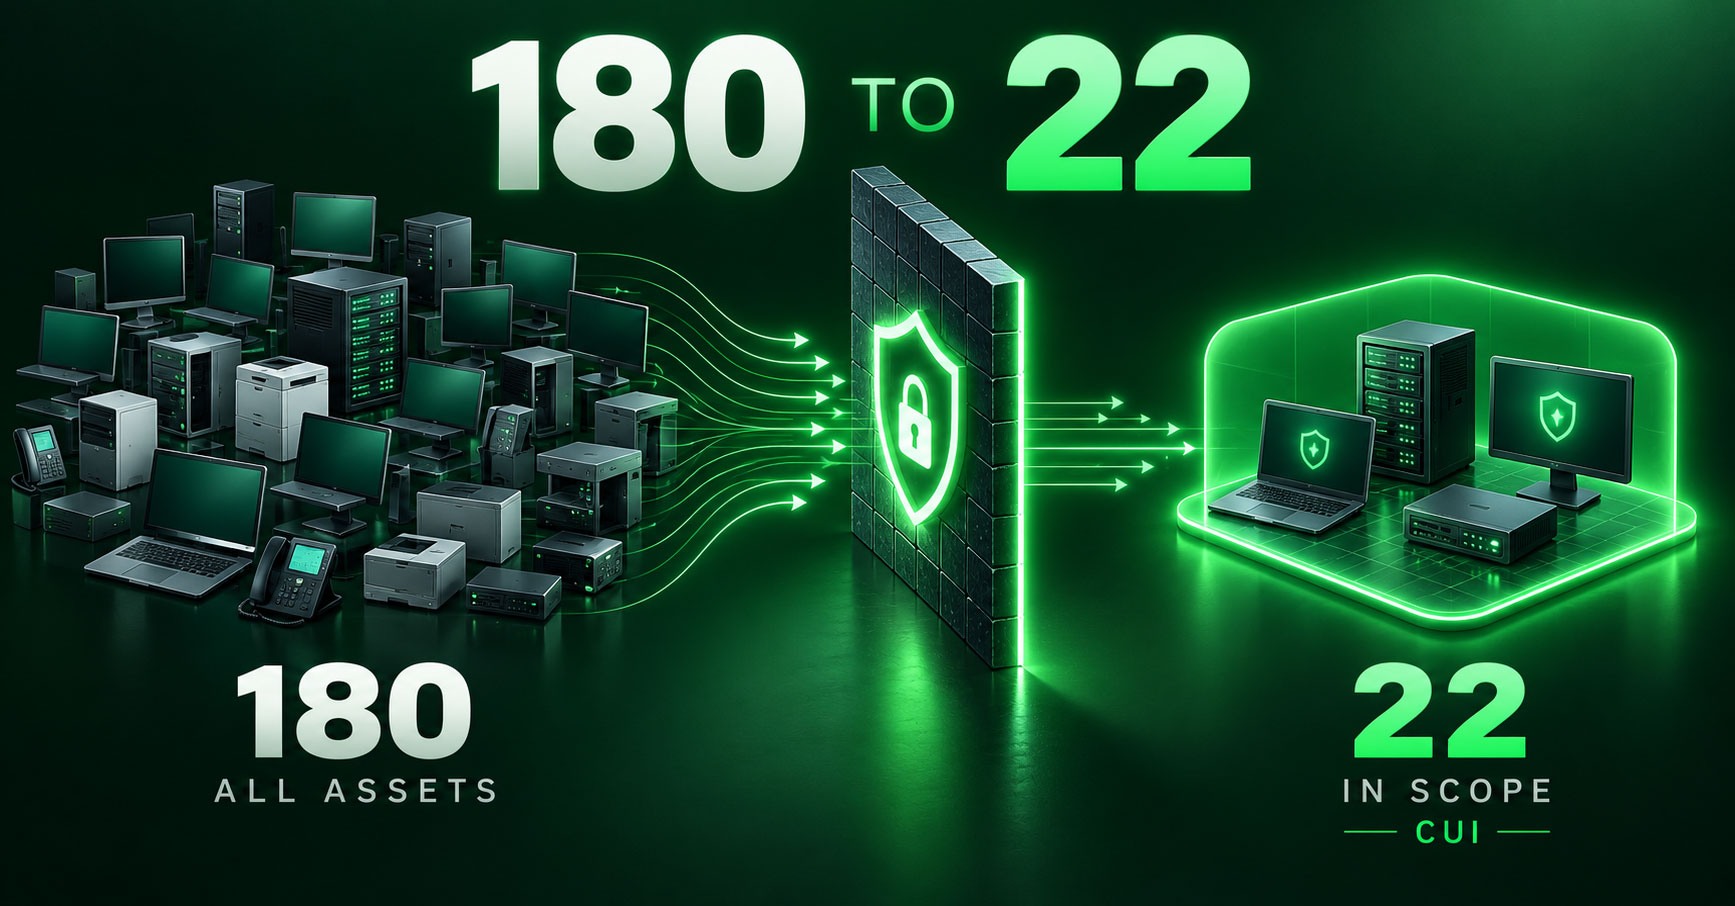
180 assets, and almost none of them needed to be
Picture a small machine shop, around forty people, precision parts for defense primes. This is a composite, but the numbers are real from cases like it. They’d handled CUI for years: drawings, tolerances, specs, all living on a shared file server the whole building could reach. One flat network. Shop floor terminals on the same wires as the accounting laptops, the ERP, the owner’s PC. When they counted, the inventory came back at 180 assets, and nearly every one of them was in scope.
Not because 180 machines handled CUI. Because they could reach it. Under the scoping rules, if a device can reach CUI and you can’t prove otherwise, it’s in scope. Their network had never been designed with any separation, so CUI touched everything by default. The assessment quote reflected all 180 assets, and the owner’s response was, more or less, that’s not happening. That wasn’t a reaction against security. It was a reaction against treating the entire business as though every asset needed the same protection as the ones that actually held CUI.
So they stopped trying to fix 180 things and did one thing instead. They built a wall around the twenty-two assets that actually touched CUI, two engineering workstations, a file server, the network gear and access controls around them, and proved the other 158 couldn’t reach it. Same requirements. Same rigor. Applied to twenty-two assets instead of a hundred and eighty.
Before: one flat network
Nearly every asset in scope, because nearly every asset could reach the file server.
After: a walled enclave
The assets that actually touched CUI. The other 158 proven separate.
When I was the compliance lead, this was the lever I wish I’d understood sooner. The biggest thing you can do for your budget isn’t buying more security. It’s having less to protect in the first place.
The mistake is treating scope as a discovery
Here’s the mistake, and almost everyone makes it. We treat scope as a discovery: list everything we own, and whatever we find is what we have to protect. But scope isn’t something you discover. It’s something you design. You decide where CUI lives, you build a boundary around that, and everything outside the boundary, proven separate, simply isn’t assessed.
The size of the boundary sets the bill
The scope is the price.
That’s the whole principle, and everything else follows from it. Every asset inside your boundary carries a cost: controls to implement, evidence to produce, assessment time to pay for, licensing, and upkeep every year after. The cheapest control is the one you don’t have to implement. So the single most powerful move in your whole budget isn’t a purchase. It’s shrinking how much you have to protect. In the shop’s case, cutting from 180 assets to 22 didn’t just lower the assessment quote. It shrank the remediation list, dropped the secure-cloud licensing from company-wide to a handful of seats, and turned an eighteen-month ordeal into a project they could actually finish.
A new stop every Tuesday and Thursday.
Our twice-weekly series breaking CMMC down one step at a time. Opt in and we’ll send each one to your inbox.
How you actually shrink it
The mechanism is an enclave: you wall your CUI work into a small, separated environment, physically and logically, so the rest of your systems are genuinely outside it. It isn’t a product you buy. It’s a decision about where CUI lives and a commitment to enforce that line. Often it also means changing a few habits that were dragging CUI everywhere: the shop floor pulls a sanitized export instead of the live CUI file, accounting receives invoices instead of designs, remote users work through a virtual desktop so nothing lands on their laptop.
The trigger isn’t really a headcount, it’s your workflows. As CUI gets mixed into everyday business operations, riding the same networks and touched by the same people as everything else, an enclave usually becomes far more cost-effective than treating the whole environment as in scope. A very small shop with tangled workflows might benefit; a larger one with a tiny, already-isolated slice of CUI might not. Look at how mixed your environment is, not how many badges you print.
The most affordable move you can make
Here’s the encouraging part. This is one of the highest-return, most affordable decisions in the entire process, and it doesn’t take magic software. It takes drawing a line and enforcing it. You are not buying your way to a smaller bill. You’re designing your way to one.
Two honest cautions, though. Out of scope does not mean unsecured; those systems still need basic hygiene, and your prime and your insurer will ask about them. And don’t build the enclave so small that people immediately start working around it, because a drawing forwarded to a regular inbox quietly drags scope right back out. A boundary only saves you money if it’s real and people can actually work inside it.
What I would do if I were in your seat
Inventory everything first.
You can’t shrink what you haven’t counted. List every asset before you decide anything.
Ask one question of each: does this actually need to touch CUI?
Most things don’t. The answer sorts your whole environment into keep-in and design-out.
Wall the CUI work into a small enclave, and move everything else out with real, provable separation.
Small and defensible beats big and hopeful.
Change the workflows that spread CUI.
Sanitized exports, invoices instead of designs, virtual desktops for remote staff. This is the fight worth having, because the alternative is paying to assess the whole building.
Then get your assessment quote against the small scope.
Not the big one. The number you take to your CEO should reflect the boundary you designed, not the sprawl you started with.
Scope is the one lever most contractors reach for last, and it’s the one that moves the budget most. Pull it before you talk to an assessor, not after.
So here’s the question worth sitting with before you price anything: how much of what we’re about to pay to protect actually needs to touch CUI at all? Whatever’s left over is where your savings are hiding.
A few sources
- CMMC Scoping Guide (Level 2) and 32 CFR Part 170: how physical and logical isolation moves assets out of scope, and the enclave concept
- NIST SP 800-171: the requirements every in-scope asset carries, which is why fewer assets means less cost
- DoD CMMC cost analysis (32 CFR Part 170): assessment and implementation costs scale with the size of your scope

